
TL;DR
Uber says an unauthorized third party used a service provider’s compromised internal credentials to access Uber data connected to the provider. Uber confirmed to TechCrunch that the vendor was Fireworks.ai; TechCrunch reports that the stolen information included drivers’ license details. The number of affected people nationwide and the full range of data involved remain unclear.
Uber is notifying people that an unauthorized third party accessed data linked to its account at a service provider, after the provider’s internal credentials were compromised. Uber confirmed to TechCrunch that the vendor was Fireworks.ai; TechCrunch reports that the stolen information included drivers’ license data, a detail not specified in Uber’s public sample notice.

Get everyday essentials delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
In a notice filed with the California attorney general and dated November 10, Uber said a service provider alerted it on October 9 that an unauthorized third party had compromised the provider’s internal credentials and used them to access Uber’s account with that provider. Uber said it cut its data connections with the provider and opened an investigation. By October 13, the company had determined that Uber data connected to the service provider had been accessed.
The regulatory notice does not name the provider. An Uber spokesperson identified it as Fireworks.ai in a statement to TechCrunch, saying the vendor had access to some Uber data. A Fireworks spokesperson also told the outlet that the company found unauthorized access to some of its systems that affected customer data. Fireworks’ security bulletins say it identified unauthorized use of internal credentials on October 6, Pacific time, and that a third party accessed environment variables used in evaluation jobs in a limited number of customer accounts.
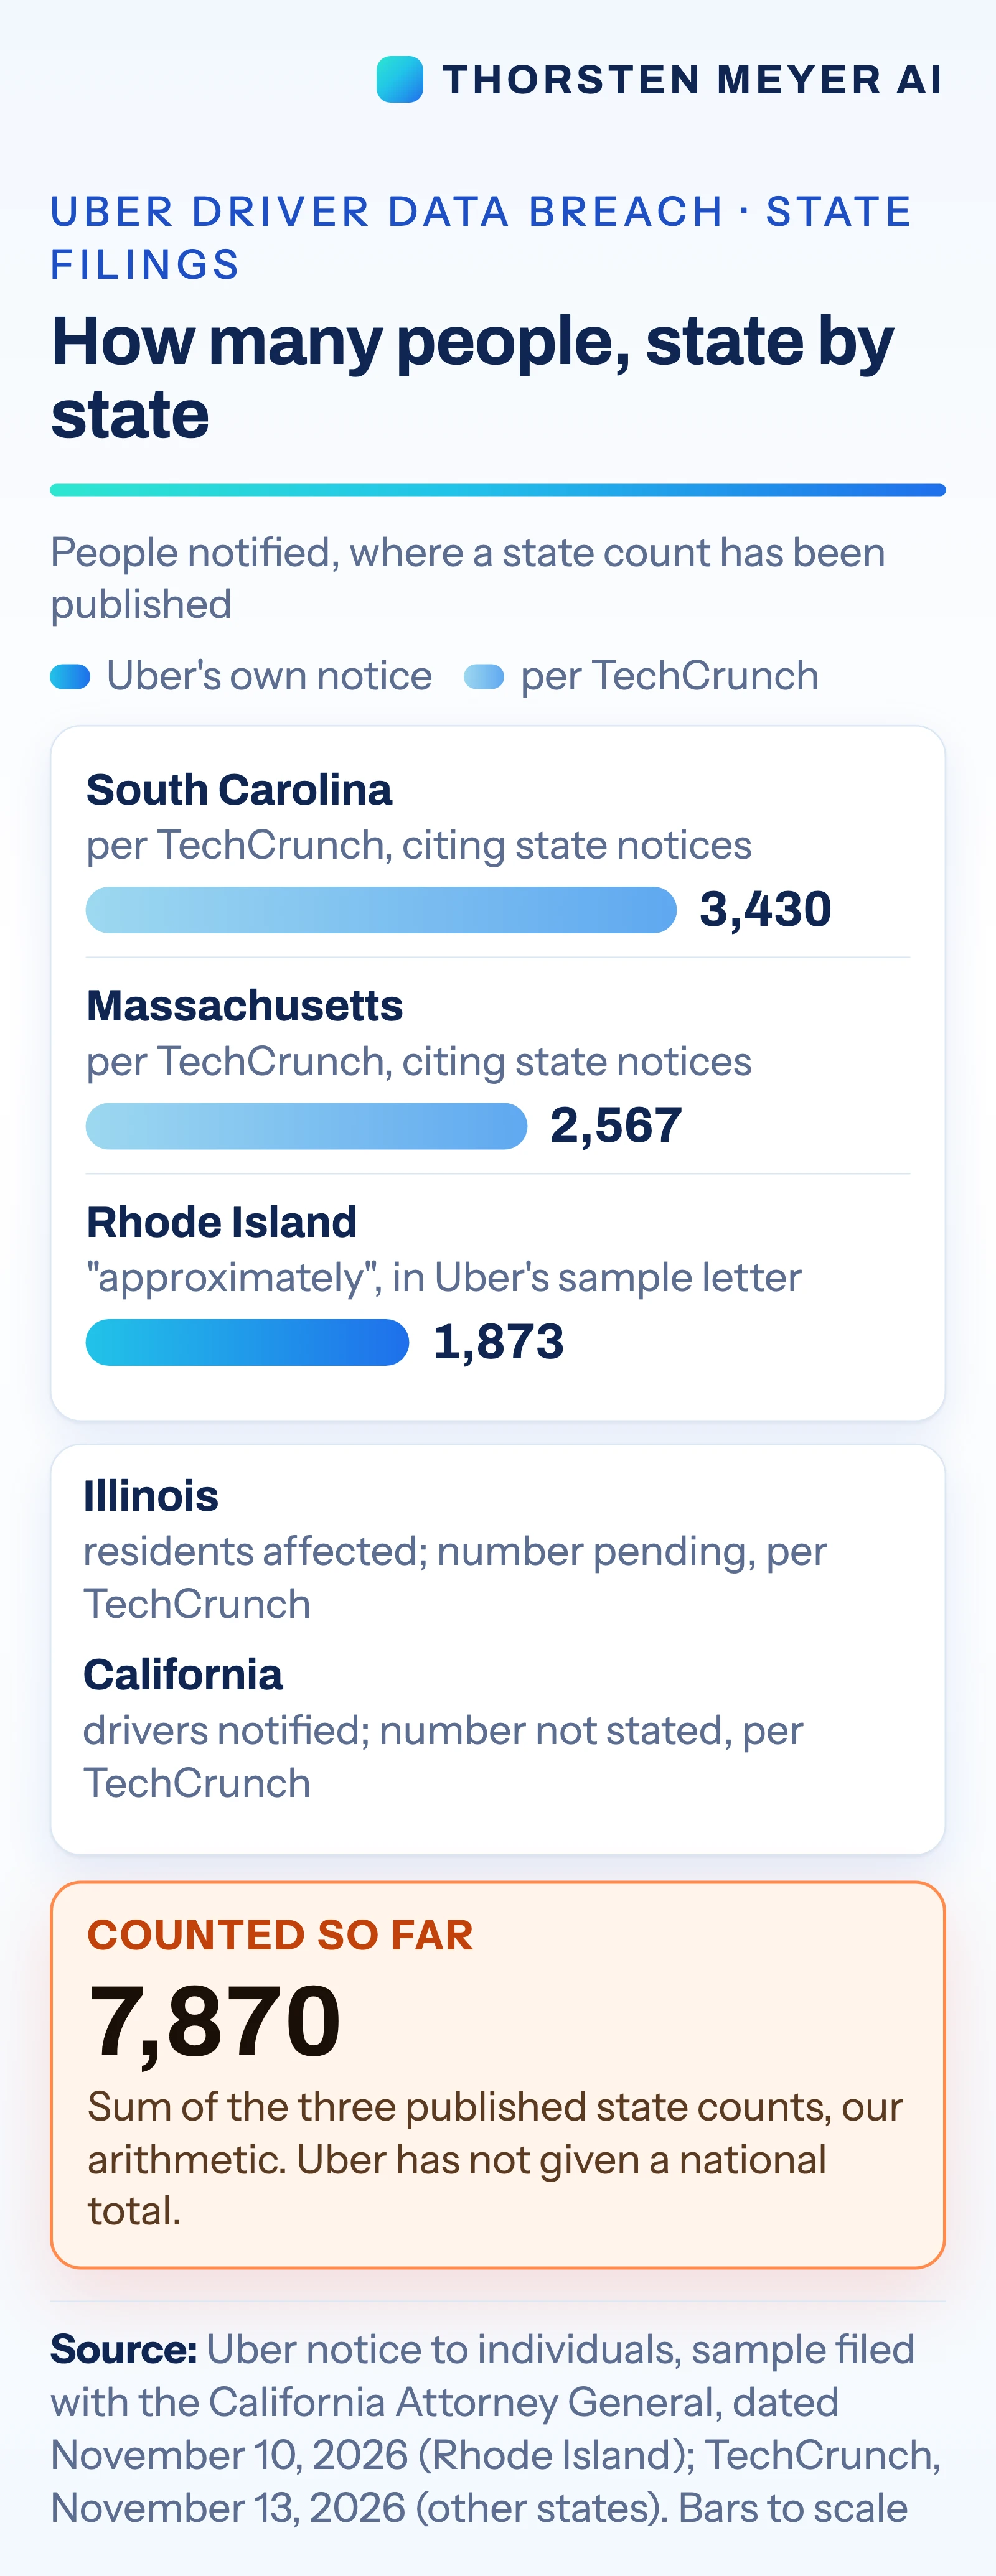
Uber’s sample letter leaves the affected-data field blank for each recipient, so it does not establish which information was involved for a particular person. TechCrunch, citing breach notices it reviewed, reports that the stolen information included drivers’ license details. Uber said about 1,873 Rhode Island residents were affected. TechCrunch reported 2,567 people in Massachusetts and 3,430 in South Carolina. Those figures total 7,870 across the three states, but they do not establish a national count.
Why License Data Matters
Drivers’ license information can be used in attempts to impersonate someone or support identity fraud. The reported exposure therefore matters to affected drivers even though Uber says it has not identified misuse of their data so far. That statement describes what the company has found to date; it does not establish that misuse is impossible or that every recipient’s information was used in the same way.
The incident also shows how information held by a company may be reachable through a vendor account. Uber’s notice describes access through compromised provider credentials used against Uber’s account with that provider. It does not say that the attacker entered Uber’s own systems. The distinction helps explain the reported route of access while leaving open what data each person’s letter identifies.
People who receive a notice have a concrete step available: Uber is offering free credit monitoring and fraud assistance through Cyberscout, a TransUnion company. The notice says enrollment must take place within 90 days of the letter date. Recipients should check their own letter for the specific data listed and enrollment instructions.
Popular right now

De'Longhi La Specialista Touch Semi-Automatic Espresso Machine with Grinder

KitchenAid 3-Piece Pasta Roller and Cutter Set for Stand Mixers

Bose QuietComfort Wireless Bluetooth Headphones – Active Over‑Ear Noise Cancelling with Mic, USB‑C Charging, Deep Bass, up to 24 h Playtime,
As an affiliate, we earn on qualifying purchases.
How Vendor Access Was Used
Uber’s filing gives October 7, 2026, as the breach date and November 10 as the date reported to California. Its attached sample letter says the provider notified Uber on October 9; Uber then severed the data connections and investigated. The investigation found on October 13 that the unauthorized party had used compromised credentials to access Uber data connected to the provider. These dates describe the sequence in Uber’s notice, while Fireworks’ bulletin dates its detection of credential misuse to October 6, Pacific time.
Fireworks provides a platform for running and customizing open AI models for businesses. Its role here is as a service provider with access to some Uber data, according to Uber’s statement to TechCrunch. The available accounts describe an attack involving Fireworks credentials and customer data; they do not explain how the attacker obtained those credentials or identify the person or group responsible.
The public sample letter does not name Fireworks or specify the data accessed. Reuters, which also reviewed the California filing, noted that the notice did not name the provider or list the data involved. The vendor’s name came from Uber’s statement to TechCrunch, while the report of drivers’ license information came from notices reviewed by that outlet. Those details should be distinguished from what Uber’s public filing itself says.
““an unauthorized third party had compromised the service provider’s internal credentials and used them to access Uber’s account with the service provider.””
— Uber, in its notice to affected people
What Each Letter Will Specify
The number of people affected across the country is not available in the cited material. Uber’s notice gives a figure for Rhode Island, while TechCrunch reports figures for Massachusetts and South Carolina. The combined total for those states is 7,870, but it should not be treated as a national count or as the full number of affected people.
The exact information accessed for each recipient is also not stated in the public sample notice, which leaves a placeholder for the affected data. TechCrunch reports that breach notices it reviewed included drivers’ license information, but the source material does not show whether every recipient’s license information was involved or what other data may have been accessed. The attacker’s identity, motive, and any use of the data are also unknown in the material provided.
Uber says it has not identified misuse to date. That is the company’s reported status at the time of its notice, not a finding that no misuse can occur. The source material does not describe any confirmed fraud tied to this incident.
Steps for Notified Drivers
People who receive an Uber letter should read the data field and follow the enrollment instructions included with it. Uber’s offer of credit monitoring and fraud assistance through Cyberscout is available for 90 days from the letter date, according to the notice. Recipients can also use the letter to confirm which information Uber says was involved in their case.
Further reporting or notices may clarify how many people were affected and what categories of information were accessed. The available source material does not give a date for additional updates from Uber or Fireworks, or describe a next investigative milestone. For now, the confirmed public account is that Uber was alerted on October 9, found access to connected data on October 13, and began sending notices dated November 10.
Key Questions
What happened in the Uber data incident?
Uber says an unauthorized third party used a service provider’s compromised internal credentials to access Uber data connected to the provider. Uber says it cut the data connections and investigated.
Was Fireworks.ai the vendor?
Yes. Uber identified Fireworks.ai as the vendor in a statement to TechCrunch. The provider is not named in Uber’s public sample notice.
Was drivers’ license information exposed?
TechCrunch reports that breach notices it reviewed included drivers’ license information. Uber’s public sample notice leaves the affected-data field blank, so recipients should check their own letter for the information listed in their case.
How many people were affected?
Uber reported about 1,873 Rhode Island residents. TechCrunch reported 2,567 in Massachusetts and 3,430 in South Carolina. The figures total 7,870 across those states; a national total is not provided.
What can affected people do?
Uber is offering free credit monitoring and fraud assistance through Cyberscout. The notice says enrollment must happen within 90 days of the letter date. Recipients should review their letter for details and instructions.
Source: Thorsten Meyer AI